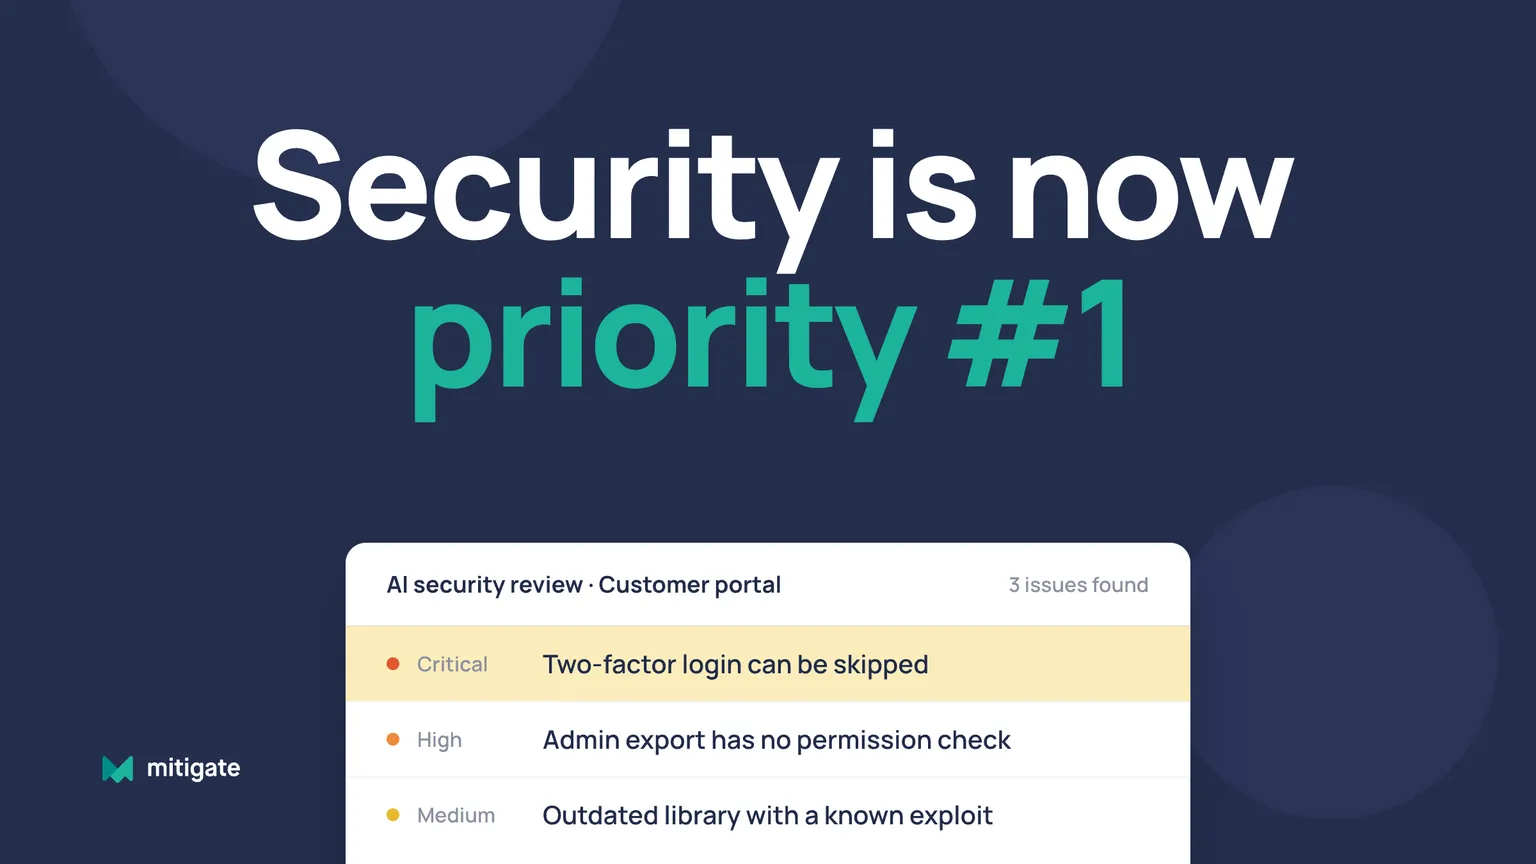
AI models can now find security flaws in source code and help write working exploits for them. Attackers use them for this, and so can the people who own the code. For anyone who owns or builds software, security has moved to the top of the list.
We wrote about AI-assisted attacks earlier this month, and we are coming back to the subject on purpose. In our own work we keep seeing how easy it has become to find security issues in code, for us and for anyone who wants to attack it.
What changed for attackers
In November 2025 Anthropic reported an espionage campaign in which attackers used its Claude Code tool against about thirty organisations worldwide. Anthropic estimates that AI did 80 to 90% of the work, with people stepping in only now and then. The AI sent thousands of requests, often several per second.
In May 2026 Google's Threat Intelligence Group described the first zero-day exploit it believes was built with AI help. Criminal groups planned to use it for mass exploitation of a popular open-source administration tool, bypassing its two-factor authentication. The flaw was in the application's logic: the developer had hard-coded a trust assumption.
There’s a misconception that the AI vulnerability race is imminent. The reality is that it’s already begun. For every zero-day we can trace back to AI, there are probably many more out there.
Attackers also move faster than patches. Mandiant's M-Trends 2026 report estimates the mean time to exploit a vulnerability at minus seven days, which means exploitation often starts before a fix is released. Exploits were the most common way into an organisation for the sixth year in a row, at 32% of the intrusions Mandiant investigated.
What changed for software owners
The same models find flaws for the people who own the code. In January 2026 OpenSSL, the encryption library behind a large part of the internet's secure connections, fixed 12 vulnerabilities. The security firm AISLE found all 12 with its autonomous AI analyzer. Some of the flaws had been in the code since 1998, in a library security specialists have examined for decades.
We see this in our own work. Mitigate has built custom software since 2011, and with current AI models we find security issues in our own code, older systems included, that would once have taken a lot of specialist time to uncover. That is uncomfortable for a software company to say. We say it because we expect the same of most systems written before these tools existed, whoever wrote them. AI also makes a first review pass cheap enough to repeat, so there is less reason to wait.
Treat it as priority one
There is a lot of noise about AI, and it is tempting to tune all of it out. Keep listening to the security part. Once AI can do most of the work of finding a flaw and exploiting it, a system that has run for ten years without an incident tells you little about its security. It may simply never have been examined with the tools attackers now use.
We encourage every software owner and development team to follow what is happening in security and act on it:
- Put security first on the plan for every system you own, especially older ones that have grown through several teams and integrations.
- Assume there are weaknesses you have not found yet, and test that assumption with an AI-assisted review of the source code.
- Keep experienced engineers responsible for the result. AI misses real vulnerabilities and reports ones that do not exist, so someone has to confirm each finding, fix it and test the fix. An empty list of findings does not prove a system is secure.
- Development teams can run the same review on new code before it ships, so fewer flaws reach production.
- Use a recognised standard to guide the review, such as version 5.0 of the OWASP Application Security Verification Standard for web applications.
- Agree how the source code will be handled before any tool gets access, and keep production credentials and customer data out of the review.
If a system you depend on has not had a security review in the last year, put one on the plan this quarter today.